Information Security · NIS-2 · ISMS

Younes Ahmadzei

Information Security Consultant

I work on the practical implementation of regulatory requirements, especially NIS-2, ISO/IEC 27001, TISAX and BSI IT-Grundschutz. My focus is on solutions that also work under the real conditions of mid-sized companies.

Portrait of Younes Ahmadzei
April 2026 21st German IT Security Congress

Featured talk

NIS-2-Implementierung im deutschen Mittelstand

At the BSI's German IT Security Congress, I presented results from my follow-up study on implementation barriers, evidence and standardised self-assessment. The contribution was nominated for the Best Student Award.
Speaking

Talks and recordings

Research findings and practical experience for professional audiences, companies and the security community.

BSides Munich · Talk

Beyond the Checkbox: Can Your NIS-2 Evidence Survive Reality?

Why the same “Yes” in an assessment can carry very different levels of confidence, and how to test the evidence behind it.

BSides Munich · Workshop

From Checkbox to Evidence: A Hands-On NIS-2 Assessment for a Fictional SME

Four-hour workshop: participants act as the assessment team and test the NIS-2 claims of the fictional company Musterwerk 180 against synthetic evidence.

Elbsides · Hamburg

Still Out of Sight? The NIS-2 Reality Check in German SMEs

Results of the second research phase on NIS-2 implementation in German SMEs.

BSI · Bonn/Online

NIS-2-Implementierung im deutschen Mittelstand

Barriers, approaches to solutions and the role of standardised self-assessment.

BSides Munich

In Scope, Out of Sight: Why NIS-2 Isn't Landing in German SMEs

Insights from outreach to 1,800 SMEs and 17 expert interviews.

WebinarNIS-2

NIS-2 in der Realität

Early experience from implementation, and where companies are currently stuck.

Practice and research

From research to a working tool

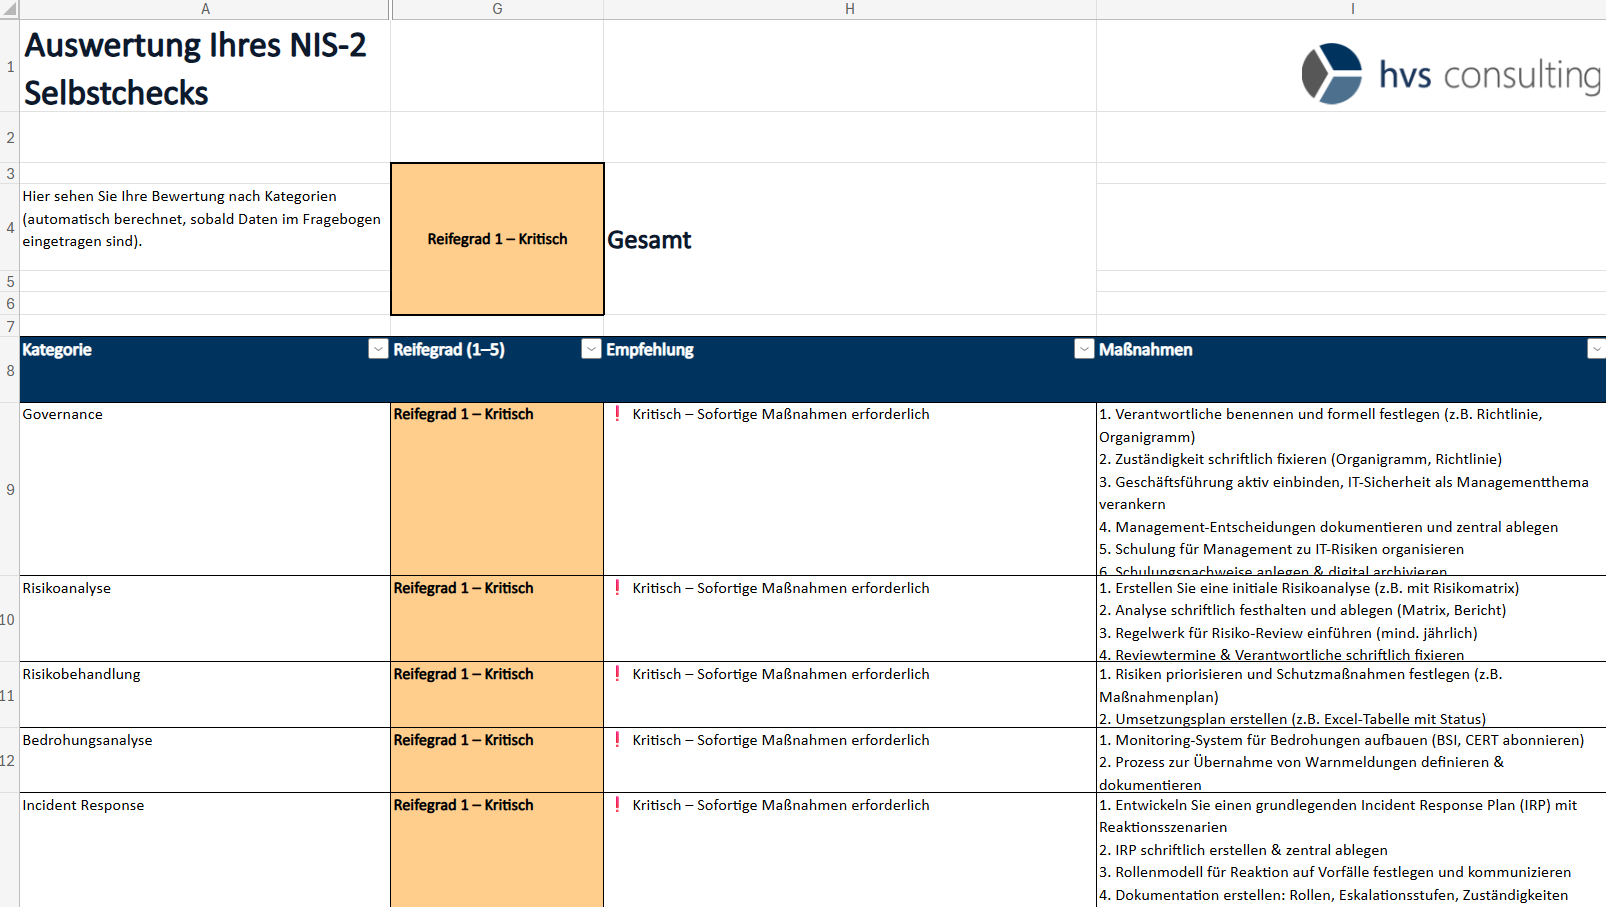
Screenshot of the NIS-2 self-assessment tool

NIS-2 self-assessment for SMEs

Structured self-assessment instead of an abstract checklist

This Excel-based maturity model grew out of my empirical research. It distinguishes between implementation and evidence, helps prioritise gaps and maps requirements to established standards.

  • 37 guiding questions on implementation and 37 mirrored questions on evidence
  • Mapping to ISO/IEC 27001, TISAX and BSI IT-Grundschutz
  • Maturity rating and concrete recommendations
  • For a pragmatic start in mid-sized organisations
1,800SMEs contacted
17expert interviews
2research phases

View methodology and development →

Contact

Professional exchange and talks

On NIS-2, information security management and the practical implementation of regulatory requirements.